|
|
 
|
|
Author
|
Topic: Sony Hack Hits Home
|
Paul Mayer
Oh get out of it Melvin, before it pulls you under!
Posts: 3836
From: Albuquerque, NM
Registered: Feb 2000
|
 posted 12-19-2014 05:49 PM 


Well maybe those of us near Santa Fe, NM may get to see it on a big screen... 
quote:
Game of Thrones' George R.R. Martin offers to screen The Interview
Game of Thrones creator George R.R. Martin has offered to screen The Interview at the theatre he owns in Santa Fe following threats from the Guardians of Peace hacker group that led to theatre chains declining to show it.
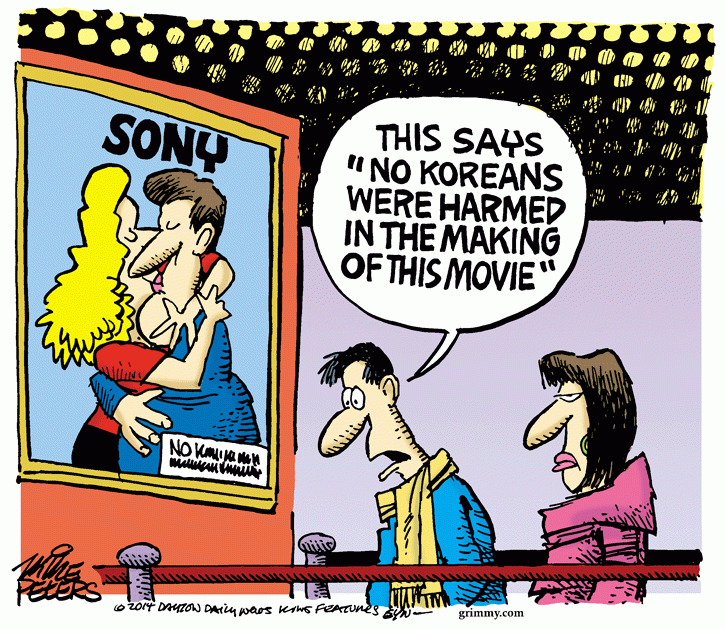
Sony Pictures cancelled The Interview's theatrical release on the Dec. 25, after major exhibitors including AMC, Regal, and Cineplex opted not to show the movie, which had drawn the ire of the mysterious hacking group that had been leaking Sony documents in the past four weeks. On Tuesday, the group threatened violence against theatres that would screen it.
Martin, however, criticized the decision to shelve the film (which is a satirical comedy about an assassination plot against North Korea's Kim Jong-un) calling it "a stunning display of corporate cowardice."
"I mean, really? REALLY??" Martin wrote on his personal blog this week. "These gigantic corporations, most of which could buy North Korea with pocket change, are declining to show a film because Kim Jong-un objects to being mocked?"
The author, who is the mastermind behind the A Song of Ice and Fire epic fantasy series that inspired HBO's hugely popular Game of Thrones show, invited star Seth Rogen to his Jean Cocteau Cinema in his hometown of Sante Fe to screen the film.
"It astonishes me that a major Hollywood film could be killed before release by threats from a foreign power and anonymous hackers," Martin wrote.
| IP: Logged
|
|
|
|
|
|
|
|
Frank Cox
Film God

Posts: 2234
From: Melville Saskatchewan Canada
Registered: Apr 2011
|
posted 12-19-2014 11:40 PM
For anyone who's interested in how this hack was done, there are numerous details provided here.
The attackers used a Server Message Block (SMB) Worm Tool which consists of five parts: Listening Implant, Lightweight Backdoor, Proxy Tool, Destructive Hard Drive Tool, and Destructive Target Cleaning Tool.
This set of programs runs only on Microsoft Windows. It uses a brute force approach to propagate through your (Windows) network, sends anything of interest that it finds along the way back to Command and Control servers, and renders the computers on the network unusable after it's been through. The C2 servers are or were apparently located in Thailand, Poland, Italy, Bolivia, Singapore and the United States.
Technically, this looks pretty cool and mighty clever. And it gives me one more reason to recommend that people stay away from using Microsoft Windows to do anything involving real work and productivity. Linux isn't perfect when it comes to security either, but it's a damn sight perfect-er than the Microsoft Windows monoculture found in many companies.
| IP: Logged
|
|
|
|
|
|
|
|
|
|
Frank Cox
Film God
Posts: 2234
From: Melville Saskatchewan Canada
Registered: Apr 2011
|
posted 12-20-2014 11:26 AM
My knowledge of Microsoft Windows is pretty thin; the last version that I actually used was Windows 98, and I didn't use it for long.
I'm no kind of a security expert so what I say here could easily be wrong in the details. If it is, someone else feel free to correct me.
When large companies set up the computers that they put onto employees' desktops, they use a standard master image to do so. Therefore, the local admin hashes will all be the same.
If you can compromise one single desktop computer (not a particularly difficult task -- you only need one out of however-many thousand) you can then extract the admin hashes for that machine and by golly they will be exactly the same on all of the machines that were set up using the master image.
Now that you're in, you can obtain the plain text password of any currently logged in account.
Think about this for a second. Who's logged into an individual workstation other than Mary Smith in Accounting? Background services require account credentials that are stored in the local Windows Registry. Domain admin is the obvious one, but there are lots of other interesting things to be found there. Anything that requires a background push or pull, really. Centrally administered security software, firewall configuration, network printing services... name your poison.
Note that we're still just looking at one single computer here, we haven't even started looking for interesting goodies on the rest of the network that we're now part of.
My impression is that basic SMB is so simple to set up that a dead dog could do it. (Never set it up myself, don't know this first hand.) "Does it work now?" "Yep." The job is now done, nobody thinks of securing it any further than that. And when you're paying someone by the hour to set it up, you don't want him "wasting time" on something that's apparently working when there are another 1298 installs that have to be completed by Friday.
Combine this with the fact that folks were apparently storing master password lists on their computers under obscure names like password.xls, and you're pretty much handing the world over on a plate.
People tend to use the same password or simple variations of the same password on multiple devices, so once you have a list of some current passwords it's easy to create a custom dictionary for whatever the Windows equivalent of John the Ripper is.

| IP: Logged
|
|
Bobby Henderson
"Ask me about Trajan."

Posts: 10973
From: Lawton, OK, USA
Registered: Apr 2001
|
posted 12-20-2014 02:56 PM
quote: Terry Lynn-Stevens
I think this is a tough one, it very well could be the start of the next World War, however North Korea really does not stand much of a chance if there was any military campaign against the country. It would be over pretty quick.
The problem is North Korea has its big brother, next door neighbor CHINA hanging close for protection. And China absolutely wouldn't put up with anyone screwing with its kid brother neighbor.
The way to get to North Korea is by getting to China first. Somehow. A good start would be all these dip shit American companies slowly pulling their manufacturing out of there. Create new product line factories in different countries elsewhere and as the old products go obsolete the Chinese factories can be shuttered. When China figures out what's up they might be willing to see its business partnership with the United States being a little more worth while than propping up a criminally despotic state via its own welfare.
Cuba all of a sudden wants to thaw its relations with the United States principally over money. They were getting a lot of aid from Venezuela. Now Venezuela's currency is virtually devalued from the bottom falling out with oil prices. Cuba has nowhere else to go. China is kind of in the same boat. They need us. Badly. Honestly, China needs us more than they need North Korea.
quote: Carsten Kurz
In a Twitter post, the internationally acclaimed author offered Sony Pictures US$100,000 to buy the movie that is believed to have sparked the cyber-theft of confidential information from the company.
Sony might as well not do shit with the movie based on that insulting offer. The Interview, whether it's a good movie or not, is actually worth a hell of a lot more money based on all the people who would want to see just out of sheer curiosity. Paulo Coelho should have coughed up another three digits to make that $100,000 offer more legitimate.
quote: Leo Enticknap
Frankly, I'm astonished that Amy Pascal has kept her job as long as this.
I expect she'll lose her job. However a lot of specific lower level employees, whose negligent computing practices contributed to this nightmare, are guaranteed to be fired.
quote: Frank Cox
The attackers used a Server Message Block (SMB) Worm Tool which consists of five parts: Listening Implant, Lightweight Backdoor, Proxy Tool, Destructive Hard Drive Tool, and Destructive Target Cleaning Tool. This set of programs runs only on Microsoft Windows.
And I thought everyone in Hollywood used only Apple branded computers. They sure make the world look like Macs are the only computers anyone can buy in all the movies and TV shows they make.

quote: Frank Cox
Technically, this looks pretty cool and mighty clever. And it gives me one more reason to recommend that people stay away from using Microsoft Windows to do anything involving real work and productivity.
I'll bash Microsoft and Windows as much as anyone. But let's be real. The most secure computing platform ever imagined will be no match against a negligent end user.
While the software the hackers used may have been Windows-based or at least designed to attack Windows-based computers, it appears very clear that bad decisions on the part of IT people and end users were the key on allowing the hackers to gain access. It sounds like all they needed to do is launch a dictionary based attack. The IT guys didn't set log-in attempt limits. The end users didn't use strong passwords.
As much as I want Microsoft to finally get its shit together with regard of eliminating all the damned holes in its operating system, in this case it sounds like Microsoft can deflect much of the blame on this hack back to Sony and its personnel.
| IP: Logged
|
|
|
|
Randy Stankey
Film God

Posts: 6539
From: Erie, Pennsylvania
Registered: Jun 99
|
posted 12-20-2014 03:57 PM
So, this whole hack was carried out by little more than a few North Korean script kiddies?
And, these little cyberpunks are essentially holding a multinational corporation hostage?
While North Korea has demonstrated that they MIGHT be able to launch a nuclear weapon, we haven't seen any real proof of that, beyond a few nuclear tests and a few test missile launches. I don't remember if they have ever put the two together and launched a nuclear warhead ON a missile. Have they?
Besides, that I haven't seen much of the North Korean military besides a bunch of guys parading around in lock-step like a bunch of Nazis, breaking bricks with their fists and busting boards over each other's heads. Teenagers do junk like that on YouTube, FFS!
Why, I bet that Sony pictures could hire a bunch of actors, special effects artists and pyrotechnicians to go to North Korea and wipe them out in a weekend. Then they could film it and make a movie out of it, while they are at it. Selling that on PPV video would quickly recover the costs of the para-military operation.
The only thing propping up North Korea is China and even THEY think of Kim Jong Un (or whoever is really running the country) like a red headed stepchild!
I think the solution, here, is to drive a wedge between China and North Korea and turn them into the "New Cuba." I think the U.S. could easily start pulling money out of China and funneling it into Cuba. They've got an impoverished working class that would be great to use as a cheap source of low-paid industrial workers.
During the next couple-few decades, Cuba could be a new banana republic and we could leave China and North Korea high and dry.
In the mean time, somebody needs to to a mash-up on "Kyle's Mom is a Great Big Bitch" and substitute "Kim Jong Un" for "Kyle's Mom."
THAT would be funny!  
| IP: Logged
|
|
|
|
|
|
|
Powered by Infopop Corporation
UBB.classicTM
6.3.1.2
The Film-Tech Forums are designed for various members related to the cinema industry to express their opinions, viewpoints and testimonials on various products, services and events based upon speculation, personal knowledge and factual information through use, therefore all views represented here allow no liability upon the publishers of this web site and the owners of said views assume no liability for any ill will resulting from these postings. The posts made here are for educational as well as entertainment purposes and as such anyone viewing this portion of the website must accept these views as statements of the author of that opinion
and agrees to release the authors from any and all liability.
|
 Home


 Printer-friendly view of this topic